Your management system

Your information security management system

One platform for your management system, with its own specific modules alongside the general modules below.

Our core

ISMS: Information security

For ISO 27001, NEN 7510 (the Dutch healthcare information security standard) and the Dutch Cybersecurity Act (the Dutch implementation of NIS2).

  • Information Security Plan with control implementation and progress
  • Statement of Applicability (SoA), generated automatically
  • Predefined controls and tasks for each standard
  • Incident and data breach reporting, including GDPR notifications
Legislation

Ready for the Dutch Cybersecurity Act and the GDPR

ComplianceGuard translates the Dutch and European obligations into concrete controls, tasks and records: you demonstrate that you comply.

Dutch Cybersecurity ActThe Dutch implementation of NIS2

The successor to the Dutch Network and Information Systems Security Act (Wbni) affects thousands of organisations in essential and important sectors. ComplianceGuard helps you with the duty of care and the notification duty.

  • Predefined controls for the duty of care, linked to your risk assessment
  • Incident reporting with the notification deadlines (early warning within 24 hours)
  • Supplier management for risks in the supply chain
  • Demonstrable evidence towards the supervisory authority through reports and a logbook

GDPRGeneral Data Protection Regulation

Get your processing of personal data in order and keep it demonstrable. From the record to the data breach notification: everything in one place.

  • Record of processing activities linked to your data collections and processes
  • Data breach registration with the notification duty towards the Dutch Data Protection Authority
  • Data processing agreements and assessments in supplier management
  • Privacy policy and procedures with version control and review
General modules

The engine under every management system

These modules work for all your standards at the same time: one way of working, whether you run ISO 27001, NEN 7510 or the Dutch Cybersecurity Act.

Clear Dashboard

See at a glance where you stand with your compliance. Real-time insight into your current risk profile, open tasks and audit findings. Clear progress and action points.

Risk Management

Identify and manage risks with a simple wizard. Your current risk level is calculated continuously on the basis of operational tasks, audit findings and registered incidents and data breaches. Parameters are fully adjustable.

Standards

Full support for ISO 27001, NEN 7510 and the Dutch Cybersecurity Act. Predefined controls, tasks and templates for each standard, plus your own standards.

Asset Management

Register and classify your assets: data, applications, hardware and contracts. With ownership, data classification and links to risks and controls, in line with ISO 27001 (A.8).

Task Management

Keep track of all compliance tasks. Automatic reminders and clear deadlines for your team.

Incident Reporting

Register and handle security incidents in line with Dutch legislation. GDPR notifications made easy.

Audit Management

Plan and carry out audits with a complete system for findings, follow-up and reporting. From planning to final report.

Document Control

Central document management with version control, templates and collaboration. You can also link documents held elsewhere, such as SharePoint or Google Drive: external references run fully within the status and review workflow.

Management Review NEW

Generate the management review almost automatically, filled with current data from across your management system in line with chapter 9.3. Management assesses, decides and signs off, including action points with an owner and a deadline and export to Word.

Supplier Management

Manage and assess suppliers on compliance. Risk profiles, assessments and tracking in line with ISO 27001, NEN 7510 and NIS2.

Reporting & Analytics

Extensive reports and dashboards for management. Export to CSV, Excel and PDF for the board and auditors.

Examples

This is what it looks like in the tool

An impression of the dashboard, risk management and the business impact analysis. Clearly arranged, in the same way of working for all your standards.

Dashboard
Risk level
Low
Compliance
86%
Open tasks
12
Findings
3
ISO 2700192%
NEN 751078%
Dutch Cybersecurity Act64%

Clear dashboard

Real-time insight into risks, tasks and the progress for each standard.

Business Impact Analysis
ProcessRTOCriticality
Order processing4 hoursHigh
Invoicing24 hoursMedium
Customer portal8 hoursHigh
Reporting72 hoursLow
Payroll processing48 hoursMedium

Business Impact Analysis

Determine the recovery time objective (RTO) and the criticality for each process.
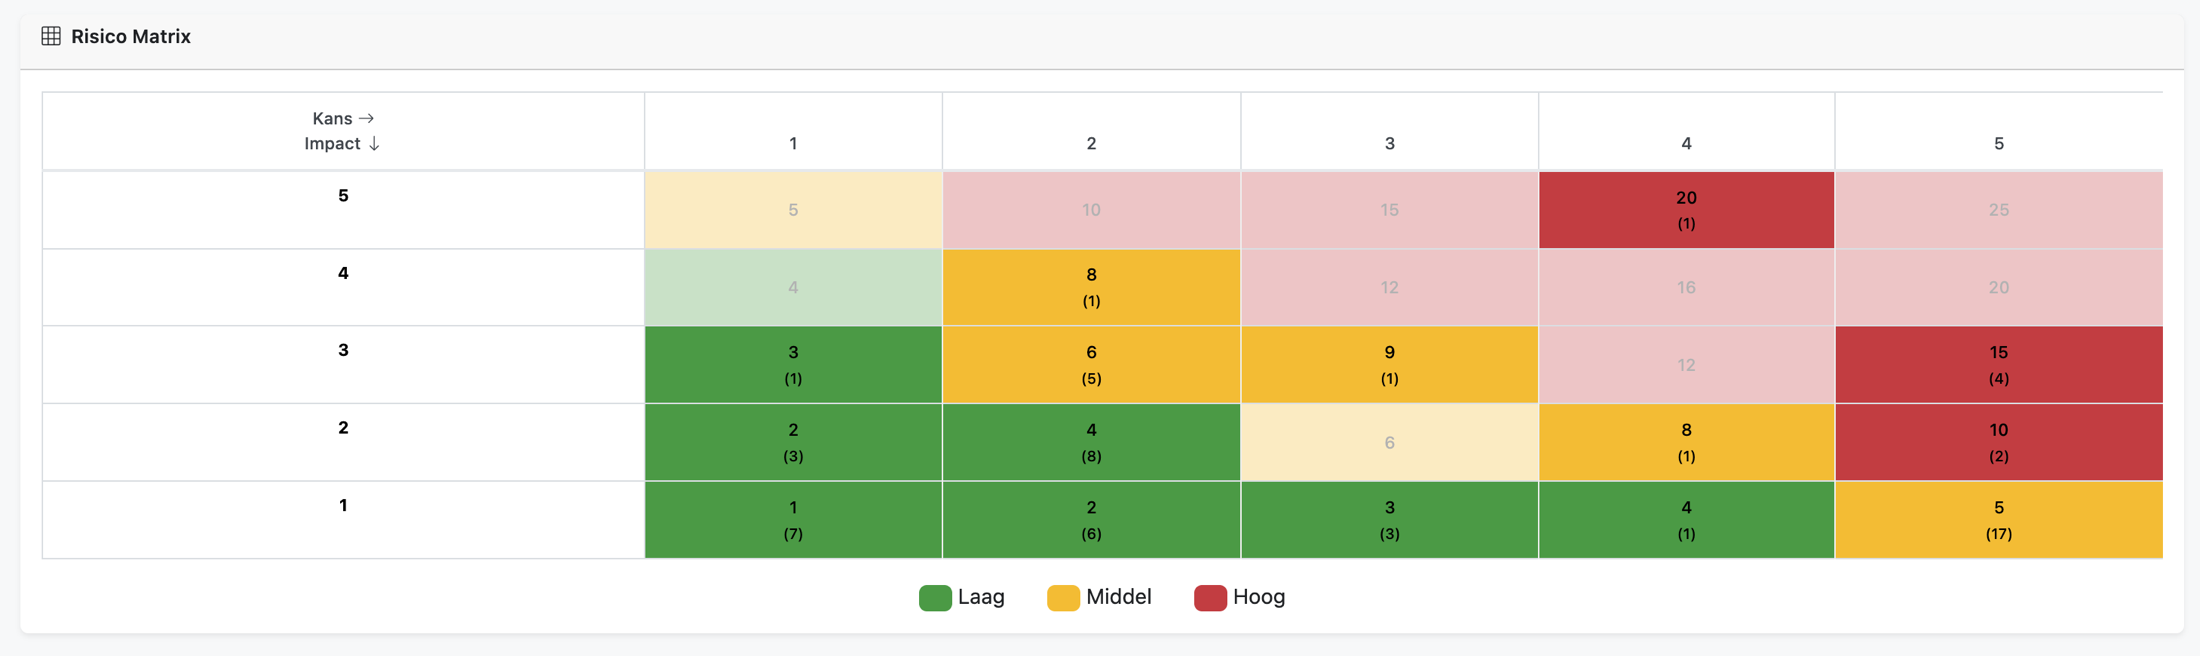
Risk management
Risk matrix in ComplianceGuard: likelihood times impact in a 5x5 matrix, with the score and the number of risks in each cell

Risk management

Risks in a 5×5 matrix. The level is recalculated continuously.

The risk dashboard: static and dynamic

Alongside the classic risk overview, the dynamic dashboard continuously recalculates your baseline risks into a current picture based on incidents, tasks and audit findings.

Risk Dashboard
Total
116
Low
32
Medium
77
High
7
Resolved 70%
In progress 20%
Open 10%

Risk dashboard

Totals, status distribution and the risk matrix in a single overview.

Dynamic Risk Dashboard
Baseline risk
34Low
70Medium
4High
Current risk
30Low
69Medium
9High
ThreatCurrentStatus
Ransomware infections15In progress
Inadequate backup procedures12Open
Disruptions caused by IT12Open
Phishing or social engineering9Resolved

Dynamic risk dashboard

Baseline risks are adjusted automatically into a current picture.

Incident factor

Based on reports linked to the threat within 90 days. Raises the risk by 10 to 30%.

Control factor

Based on overdue operational tasks from linked controls. Raises the risk by 15 to 30%.

Audit factor

Based on open audit findings within 365 days. Observations +10%, non-conformities +40%.

Illustrative examples. How things appear in your own environment depends on your standards and settings.

Supporting

Everything in one system

Security controls

Keep track of which security controls you have put in place and their status.

Policies & Procedures

Central management of all your policy documents with version control.

Backup & Archive

Automatic backup of all your compliance data and documents.

Convinced? Try it yourself.

Try all modules free for 30 days. No obligations.

Request a Demo